Blog
Monitoring Docker, OpenShift, Kubernetes and Linux - Version 5.22
Version 5.22 of our applications, configurations, and Collectord is now available. In this blog post, we will cover some highlights of the release.
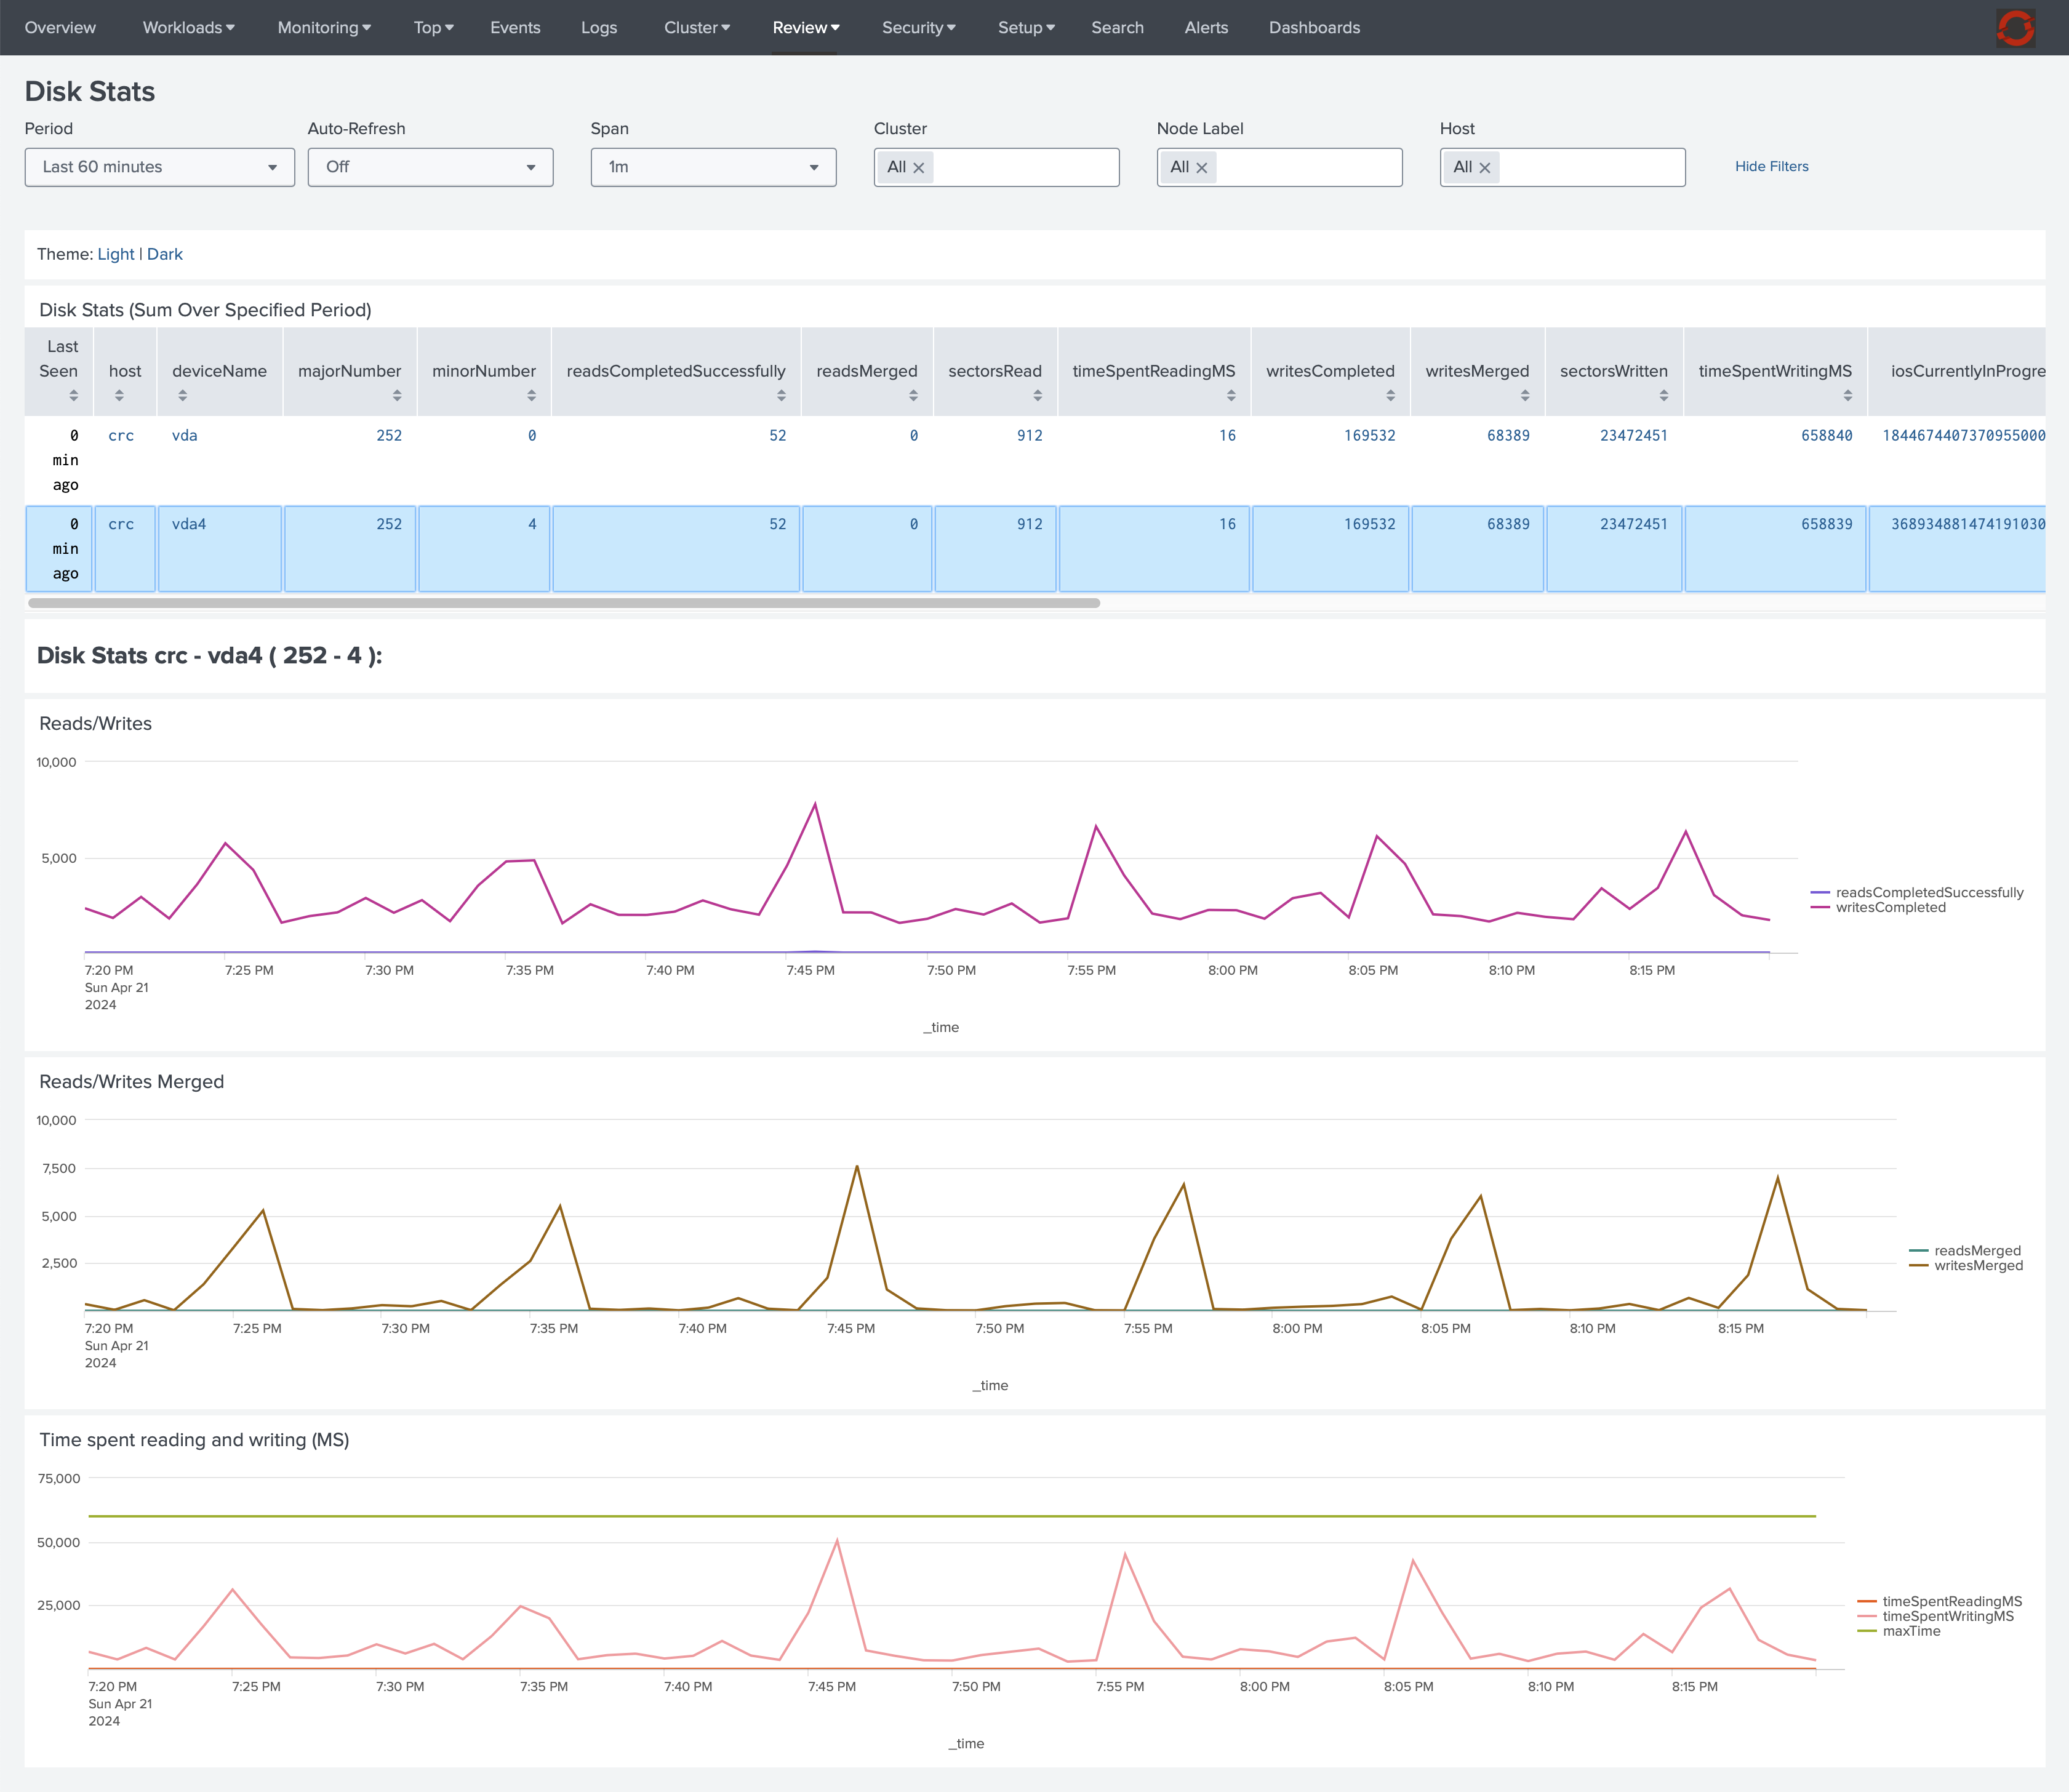
Disk Stats Dashboard
Under Review->Disk Stats you can find a new dashboard showing statistics of all the mounted disks on the host.
User defined Splunk outputs
We have received this feature request from a few customers, and we are happy to announce that it is now available.
Users can define a Splunk output with the CustomResourceDefinition (CRD) SplunkOutput in their namespace. For example
1apiVersion: "collectord.io/v1"
2kind: SplunkOutput
3metadata:
4  name: splunk-user-output-for-deployment
5spec:
6  token: 1a8b9c3e-7789-4353-821f-15b9662bac99
7  url: https://splunk.example.com:8088/services/collector/event/1.0
8  insecure: true
Similarly to how you can reference the default Splunk outputs defined in the ConfigMap, you can reference them with an annotation
1apiVersion: apps/v1
2kind: Deployment
3metadata:
4  name: long-running
5  annotations:
6    collectord.io/output: splunk::user/default/splunk-user-output-for-deployment
7spec:
8  ...
You define it as splunk::user/<namespace>/<name>.
To use this feature, you need to update your configuration file and include the definition of the CustomResourceDefinition SplunkOutput.
Other significant changes
- Monitoring Kubernetes and OpenShift applications show Pod Ownership, PriorityClass and Pod Requests and Limits in the Workload dashboard.
- Added additional metrics CPU IOWait, Steal and Idle.
- You can blacklist labels from forwarded metadata.
- New diagnostic: CPU Vulnerabilities.
You can read all other changes and bug fixes in the release notes below.
Links
You can find more information about other minor updates by following the links below.
Release notes
- Monitoring OpenShift - Release notes
- Monitoring Kubernetes - Release notes
- Monitoring Docker - Release notes